
Patient communication, handled with care.
Help protect sensitive patient communications while keeping email workflows familiar. Staff keep their inbox; patients get a link and a code instead of another account.
Enter your one-time code
Sent to j••••@example.org
Open messageWhat we hear from teams like yours.
Patient details travel by email
Lab notes, referrals and billing questions end up in email whether you planned for it or not.
Patients won't install anything
A portal account or plugin just to read one message means calls to the front desk.
Phishing targets clinics
Spoofed supplier and insurer emails aim at busy staff.
Small IT, big responsibility
Many practices have one IT person (or a provider) and no time for a complicated platform.
Practical protection, clearly licensed.
Hold PHI for the portal
Tag a message [secure] and it waits, encrypted, on your gateway. The patient opens it with a one-time code.
ProfessionalFilter what comes in
Spam scoring, DNS blocklists and SPF, DKIM and DMARC checks before mail reaches staff.
CommunityKeys on your host
Stored messages are encrypted with a key generated on the gateway. It never leaves it.
Every planAudit trail
Every configuration change is logged and exportable for your records.
Every planFamiliar for staff. Visible for IT.
Staff keep their email client. Administrators get a console that shows what was held and why.
Explore the product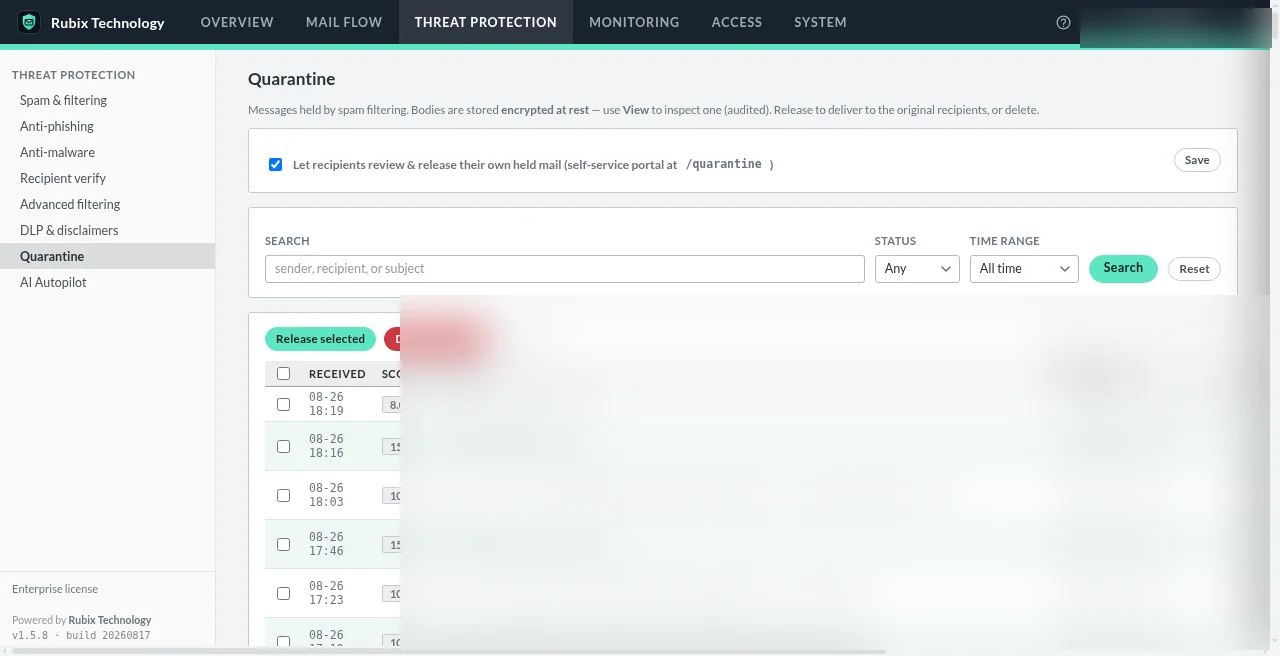
A day in the life.
A referral with test results
The clinician types [secure] in the subject. The specialist's office receives a notification, enters a code and downloads the attachment.
A patient replies with a question
The patient replies in the portal; the reply arrives in the clinician's normal inbox.
A fake “insurance portal” email
SPF and DMARC failures plus phishing signals push it over the threshold and into quarantine for review.
Know the boundaries.
We'd rather you hear the limits from us.
- Built to support HIPAA safeguards, not a certification. Your compliance obligations stay with you.
- Use your own policies and any required agreements, such as a BAA, with every vendor in the path.
- Messages are encrypted at rest; envelope metadata (sender, recipient, subject) stays searchable.
- The website contact forms aren't for PHI. Please don't send patient data through them.
Healthcare questions
Is Secure Message HIPAA compliant?
No email product can be HIPAA certified, and we don't claim it is. Secure Message is built to support HIPAA safeguards: encryption at rest under your keys, audit logs, access controls and a message path on infrastructure you own. Compliance depends on how you configure and operate it, and on your own policies and agreements.
Do patients need an account to read a message?
No. With Professional, they open a link and enter a one-time code sent to their existing inbox.
Does it work with our current email provider?
Yes. It's a gateway in front of the mail you already run, no mailbox migration.
Which plan do we need for secure patient messages?
Professional ($690/year, up to 10 domains, licensed for up to 100 users). Community covers inbound filtering only.
See it with your own mail flow.
A short demo, tailored to how your team actually sends and receives email.